
Compliance playbooks, CMDB deep-dives, and field notes from the Qbilon team. Articles are published in German.
In most IT departments, work is heavily organized into projects. There is a start date, a defined budget, milestones, and an end date. You migrate the old ERP system to the cloud – project completed.…
Budget negotiations for IT security and architecture management often follow a grueling pattern. The Chief Information Security Officer (CISO) or Enterprise Architect stands before the Chief…
The toolbox of a modern Chief Information Security Officer (CISO) is packed. According to industry studies, large enterprises use an average of 40 to 70 different security tools. There are solutions…
When IT managers talk about the security of their network, they often use the metaphor of a castle. They speak of high walls (firewalls), deep moats (network segmentation), and vigilant guards on the…
Whenever a new technology category conquers the IT market, a certain degree of confusion regarding the distinction from existing systems naturally arises in the first few months. The rapid rise of…
In the world of IT security, hardly a year goes by without a new, complicated acronym. While concepts like EDR (Endpoint Detection and Response) or IAM (Identity and Access Management) have long…
If you have read technology blogs, studied analyst reports (such as those from Gartner), or attended a cybersecurity conference in recent months, you have almost certainly stumbled across a new…
If you ask an IT veteran to describe their associations with the term "Configuration Management Database" (CMDB), words like cumbersome, outdated, bureaucratic, or project graveyard are often…
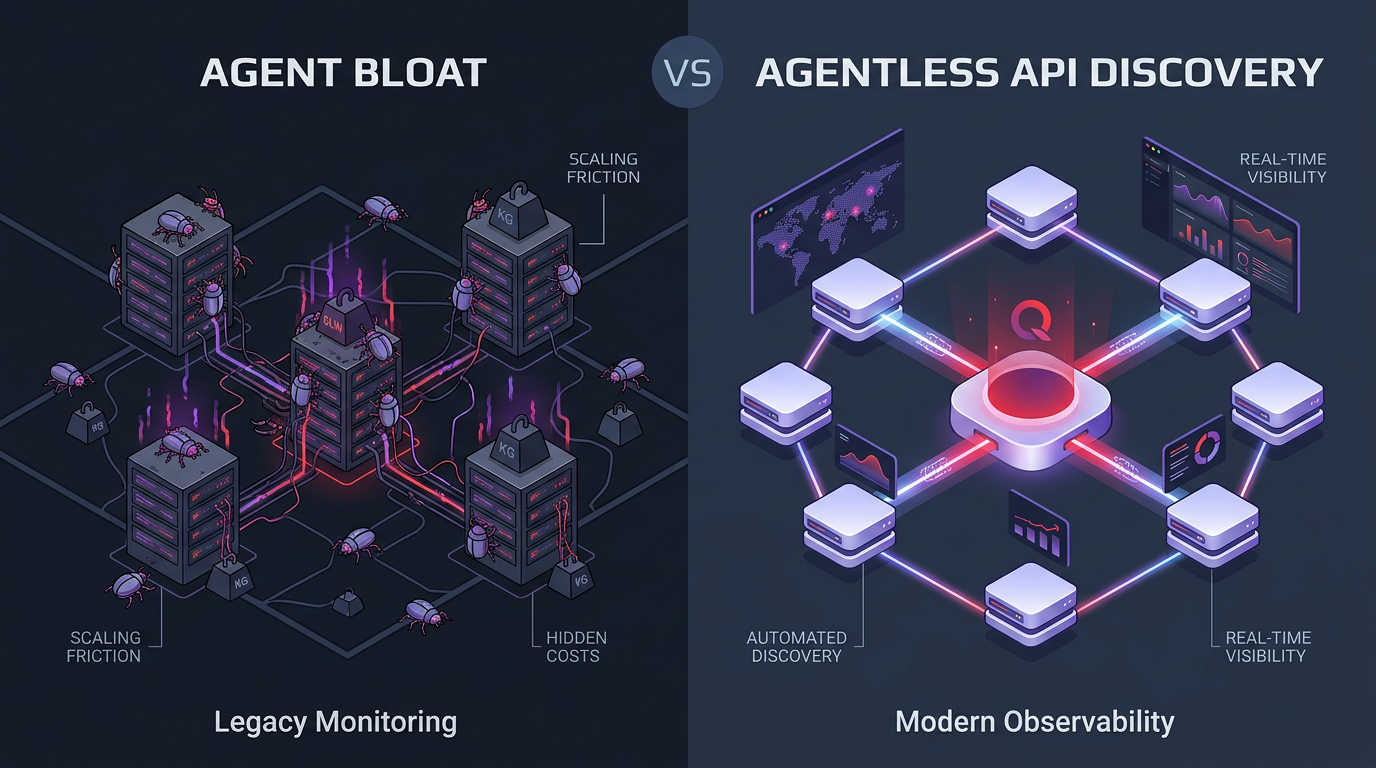
In the effort to establish full transparency and security in IT networks, companies have often resorted to a nearby but ultimately extremely painful method in recent years: the mass rollout of…
The role of the Chief Information Security Officer (CISO) has undergone a remarkable metamorphosis over the last decade. From a highly specialized "Chief Firewall Administrator" in the background,…
In large IT organizations, there are often departments that sit physically close to one another but, in practice, work as far apart as if they were on different planets. A classic example of this…
When you ask IT managers to describe their greatest professional trauma related to compliance frameworks (such as NIS 2, ISO 27001, or TISAX), the answer is rarely: "Defining the security policies."…
One email a month: compliance playbooks, CMDB deep-dives, and the occasional Qbilon behind-the-scenes. No spam, unsubscribe anytime.