Preparing for CAASM: What You Need to Know About the New Security Trend
Preparing for CAASM: What You Need to Know About the New Security Trend
If you have read technology blogs, studied analyst reports (such as those from Gartner), or attended a cybersecurity conference in recent months, you have almost certainly stumbled across a new acronym: CAASM.
Spelled out, CAASM stands for Cyber Asset Attack Surface Management. It is currently being hailed as the savior for overburdened security teams and the logical answer to the spiraling complexity of hybrid IT landscapes. Analysts predict that in the next two years, hardly any major company will be able to do without a CAASM strategy.
But as with every new trend in IT, there is a lot of confusion mixed with aggressive marketing. Is CAASM just a new buzzword for an old CMDB? Does it replace the vulnerability scanner? And above all: How do you prepare as an organization for this trend? In this post, we demystify the topic and explain why CAASM is not a product that you simply "install," but a strategic capability for which you must systematically prepare.
The Core Problem That CAASM Solves
To understand CAASM, we must look at the problem that classic IT security often despairs of today: the massive increase in the so-called "attack surface."
Only a few years ago, a company's attack surface consisted of the firewalls around the local data center and the employees' laptops. Today, the attack surface has exploded. It includes:
- Hundreds of AWS, Azure, and Google Cloud instances.
- Thousands of SaaS applications (often as shadow IT).
- IoT devices and production facilities (IT-OT convergence).
- External APIs and microservices.
- Home office routers and private end devices.
For hackers, this is a paradise. They only need to find a single tiny, unprotected spot in this vast universe. Security teams, on the other hand, have often lost track. They operate excellent tools (EDR, firewalls, vulnerability scanners), but these tools work in isolated silos. They do not provide a coherent picture.
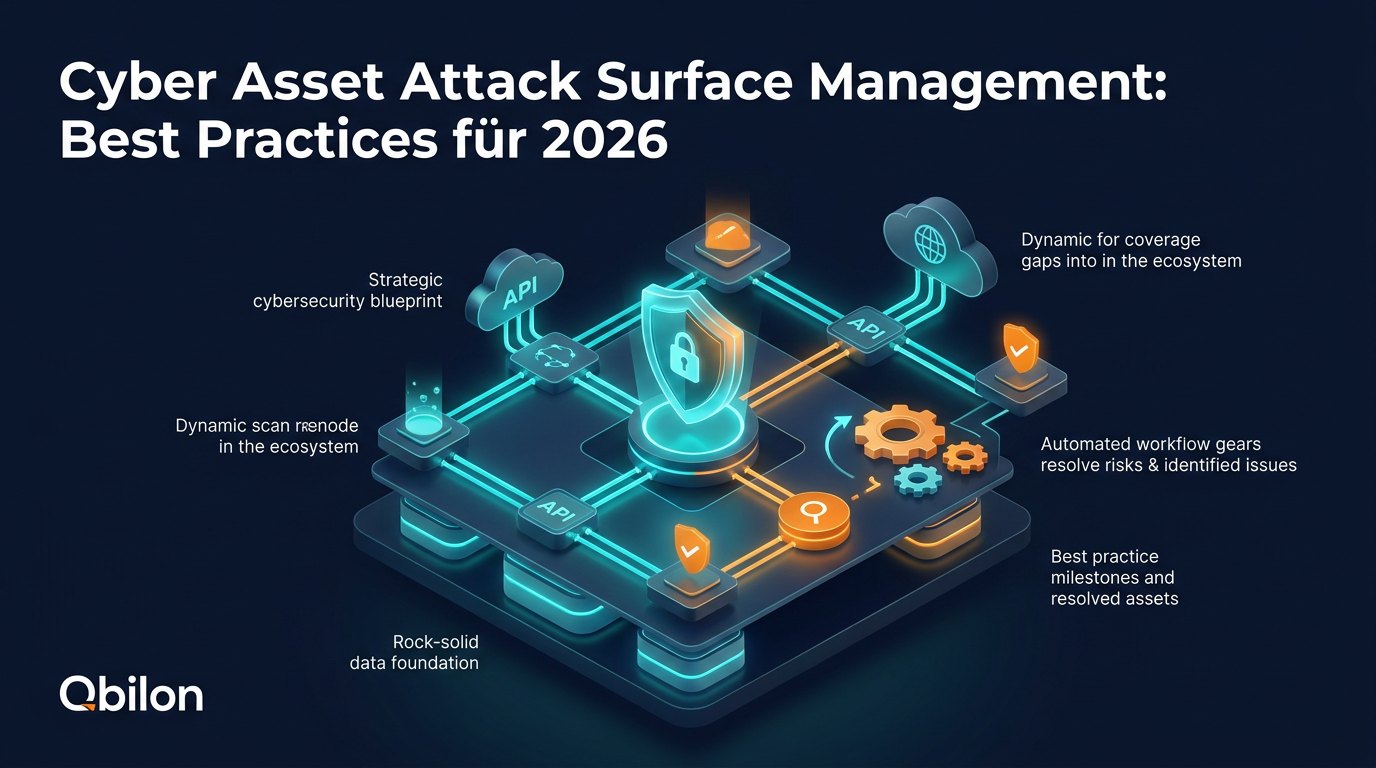
CAASM solves this problem through radical data aggregation. The basic idea: you connect all existing IT and security tools via APIs to a central platform. This platform compares the data and uncovers discrepancies.
Tool A (the cloud console) says: "We have 100 servers." Tool B (the security software) says: "I am protecting 90 servers." CAASM immediately concludes: "We have 10 unprotected servers. Here are the IP addresses for immediate remediation."
Why You Can't Simply "Buy" CAASM
The temptation is great to simply approve a budget for a "CAASM tool" and consider the problem solved. But that's not how it works in reality. CAASM is highly data-driven. The infamous IT law "Garbage in, Garbage out" applies here relentlessly.
If you try to build a CAASM strategy without first doing your homework in fundamental IT Asset Management, the project will fail.
Preparation Step 1: The Operational CMDB as a Foundation
Before you can aggregate security context (vulnerabilities, EDR coverage), you need a reliable, automated inventory of your operational basis. A CAASM solution needs a "Single Source of Truth" to know who an asset belongs to (ownership) and how critical it is for the business. If your CMDB today consists of manual Excel lists, any CAASM initiative will lead to nothing.
Preparation Step 2: Open APIs and Integrations
CAASM lives on connectors. You must ensure that your primary systems (your identity management, your cloud provider, your vulnerability scanners) have clean, readable APIs. Preparing for CAASM means breaking down silo thinking in the minds of department heads: network, cloud, and security teams must be willing to let their data flow into a central data lake.
Preparation Step 3: Establish Historization
Attack surfaces change hourly. A truly powerful CAASM approach doesn't just show you that a server has an open security vulnerability today. It shows you when that vulnerability was created and how long it went unnoticed. You must establish this temporal dimension (time machine) in your IT documentation now (e.g., for NIS-2 audits), so that CAASM can build on it later.
Conclusion: The Journey Is the Reward
CAASM is undoubtedly the future of proactive cybersecurity. It ends the guesswork and finally gives CISOs an unvarnished view of their company's true vulnerability.
However, the path there inevitably leads through professional, automated IT Asset Management. Companies that use a dynamic, integrated platform like Qbilon today to secure their NIS-2 compliance and historize their infrastructure have already done the most important preliminary work. They have created the data basis on which CAASM can unfold its full protective potential next year. Prepare your data – the security trend of the decade is just around the corner.