
CAASM for Mid-sized Businesses: Enterprise Security for Limited Budgets
CAASM for Mid-sized Businesses: Enterprise Security for Limited Budgets
Cyber Asset Attack Surface Management (CAASM) has become one of the defining topics in cybersecurity over the past few months. However, when you read the case studies and success stories of large providers, it's easy to get the wrong impression: CAASM looks like a luxury problem. It seems as if the concept was developed exclusively for Fortune 500 corporations, global banks, and tech giants with hundreds of security analysts and unlimited IT budgets.
For the IT manager of a medium-sized mechanical engineering company with 800 employees, two locations, and a three-person IT team, this often sounds like science fiction. The reaction is usually: "We have neither the money for giant security platforms nor the manpower to operate them. CAASM is a league too big for us."
This misconception is fatal. The reality is quite different: Mid-sized businesses need CAASM even more urgently than large corporations. In this post, we dispel the myth of "Enterprise-only" security and show why automation—especially given tight budgets and the skills shortage—is the only way out of the compliance and security trap.
The Threat Makes No Distinction
The first reason why mid-sized businesses cannot ignore CAASM is the asymmetric threat landscape. Cybercriminals, ransomware syndicates, and automated bot networks do not distinguish between a DAX corporation and a medium-sized automotive supplier.
Quite the opposite: Mid-sized businesses are often viewed as the "soft target" in the supply chain (Supply Chain Attack) to gain access to the large corporations actually being targeted. An open RDP port (Remote Desktop) or an unpatched VPN access at the supplier is sufficient. Furthermore, the NIS-2 directive is forcing tens of thousands of mid-sized companies under strict regulatory requirements for the first time. The auditor checking compliance with patch management or a gap-free asset inventory will not lower their standards just because your IT department is small. The liability (and the threat of fines) is absolutely real.
The Skills Shortage as a Driver for Automation
How is a mid-sized company with a hybrid cloud infrastructure, growing shadow IT through SaaS solutions, and Industry 4.0 machinery (OT) on the factory floor supposed to meet these requirements when no security experts are to be found on the job market?
The answer is: You can only compensate for a lack of manpower through intelligent technology.
If your small IT team spends four weeks a year manually reconciling Excel lists for ISO 27001 or NIS-2 audits, you are burning your most valuable resource. If your only security officer has to manually sift through hundreds of vulnerability scanner alerts every day (alert fatigue), they will leave the company.
How CAASM Works (and Pays Off) in Mid-sized Businesses
A modern, API-driven CAASM and asset data platform like Qbilon is not an "Enterprise monster" that requires a team of specialists. It is exactly the opposite: It is the invisible digital assistant that replaces missing specialized personnel.
This is how CAASM pays off for mid-sized businesses:
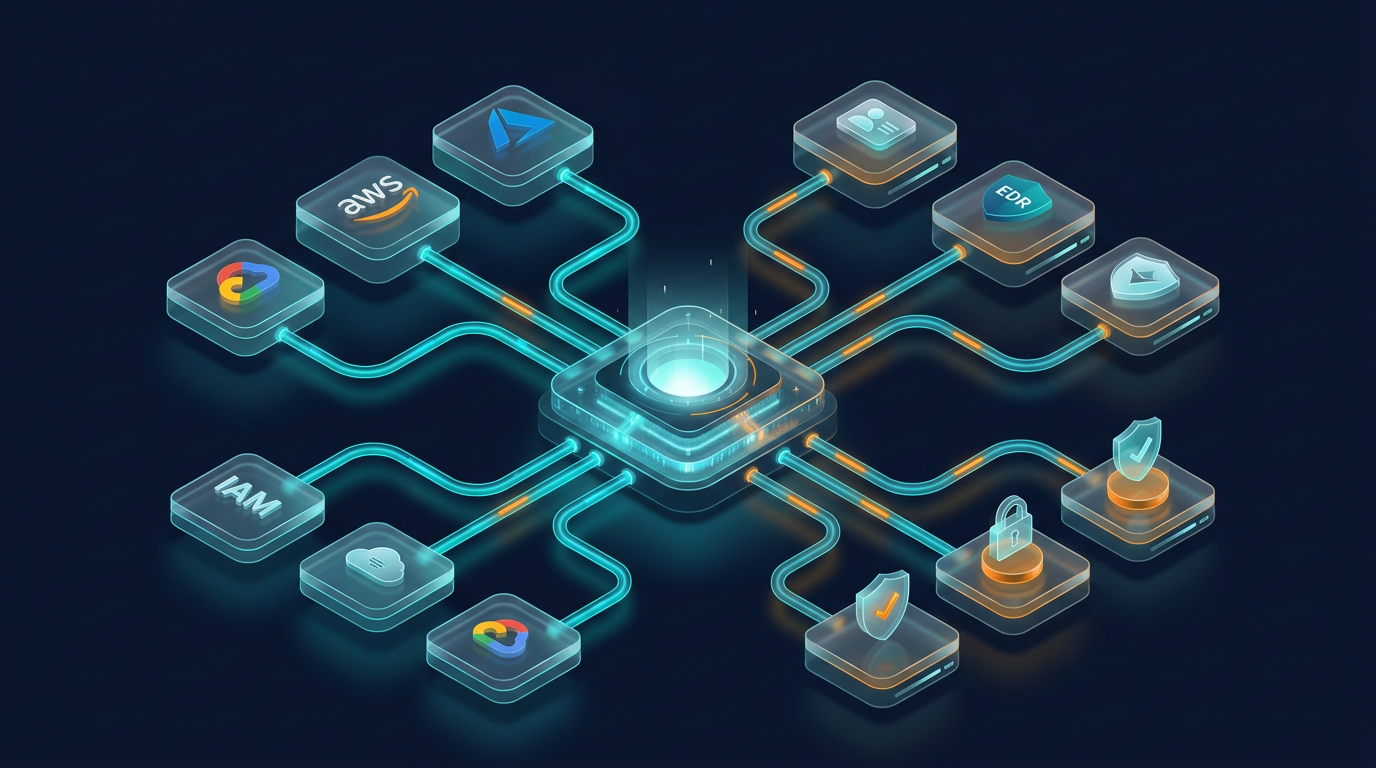
- Plug & Play Visibility (Without Agent Stress) Mid-sized businesses don't have time for six-month implementation projects. Modern platforms integrate agentlessly. You connect the platform via APIs to your Microsoft 365 (Entra ID), your VMware environment, your AWS/Azure cloud, and your endpoint protection (e.g., Defender). Within a few hours or days, a central "Single Source of Truth" is automatically created.
- Uncovering Shadow IT Without Detective Work Your team no longer needs to walk through departments and ask who is using which software. The platform automatically correlates login data and firewall traffic and spits out a list every Monday of the three new, unauthorized SaaS tools the marketing department is currently testing.
- The Double ROI: Security and FinOps Especially with tight budgets, ROI (Return on Investment) is crucial. As we have discussed in previous posts, CAASM not only identifies security gaps (missing agents, vulnerabilities) but also identifies orphaned, expensive cloud resources (orphaned assets) and unused software licenses. The solution often refinances itself in the first year through pure cost savings in the cloud and licensing areas alone.
Conclusion: Security Intelligence for Every Company Size
Don't be blinded by the marketing budgets of large corporations. CAASM is not a luxury for the top 1 percent. It is a fundamental methodology for establishing control, transparency, and security in IT networks.
Precisely because you, as a mid-sized company, have limited budgets and small teams, you cannot afford to work inefficiently. You cannot afford to maintain Excel lists, ignore shadow IT, or prepare audits manually. An automated asset platform takes the administrative burden off your shoulders, protects you from legal (NIS-2) consequences, and provides you with exactly the enterprise security transparency you need to sleep soundly at night.