Preparing for Q4: Are Your IT Data Audit-Ready?
Avoiding the Q4 War Room: How to Make IT Data Audit-Ready
It is late July. Summer vacations are just around the corner, offices are a bit emptier, and operations are running at a more relaxed pace in many places. For IT managers, compliance managers, and CISOs, right now – in this relatively quiet phase – is the most critical moment of the entire year.
Because those who do not act now will inevitably be overwhelmed by the dreaded wave that rolls relentlessly toward IT departments every year: the fourth quarter (Q4) and the associated audit season.
Whether it is the annual surveillance audit for ISO 27001 certification, the strict inspections according to BSI IT-Grundschutz, the annual financial statement audit by auditors (IT-GC), or the new, massive documentation requirements under NIS-2 – Q4 is the time when the books must be opened. In this post, we clarify what "audit-ready" IT data really means and why you must lay the foundation for a relaxed year-end closing right now.
The Traditional Q4 "War Room"
Let’s take a brief look back at how audit preparation traditionally works in many organizations. In October, it is realized that the auditors will be in the house in mid-November. Panic sets in.
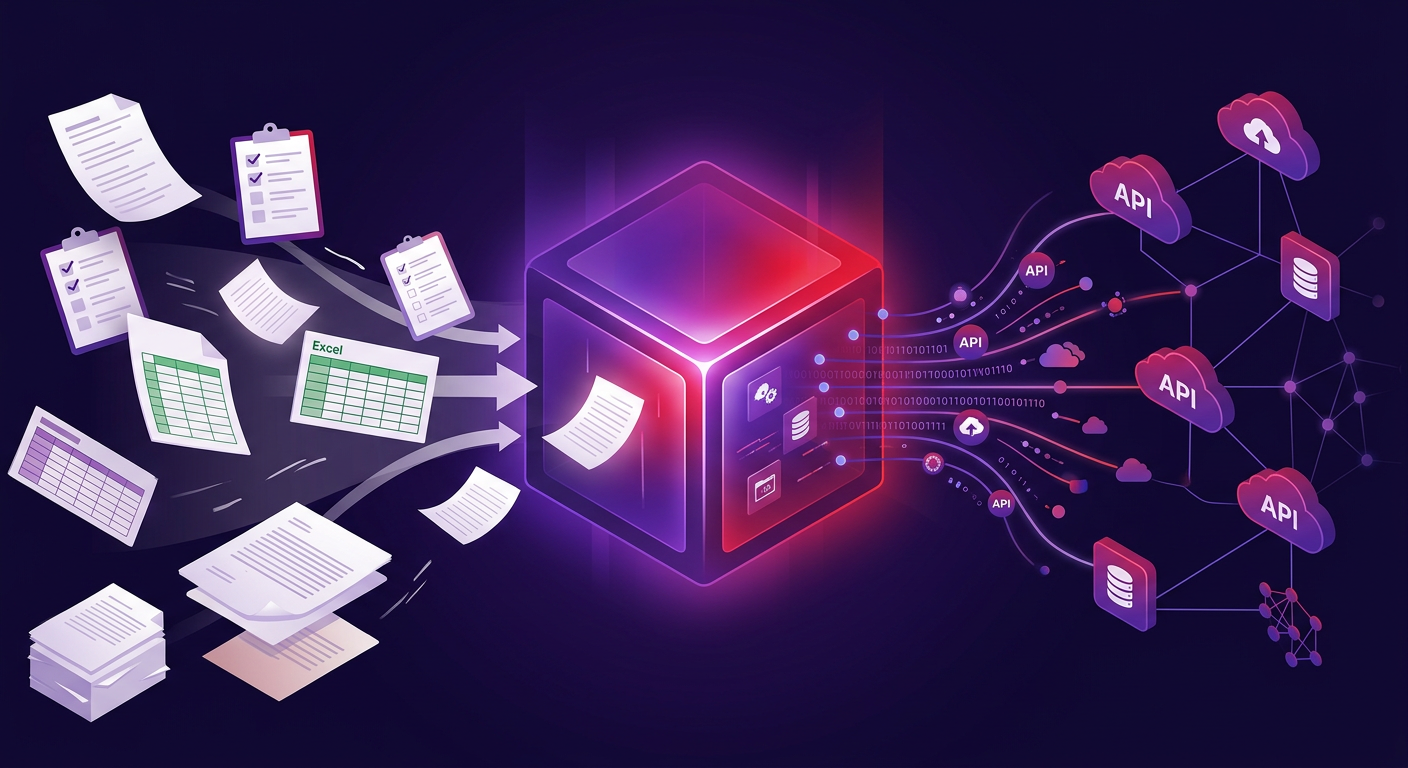
A so-called "war room" is set up. The best and most expensive IT specialists – cloud architects, network admins, and security analysts – are pulled away from their actual projects (such as cloud migration or fixing vulnerabilities). Their new, weeks-long task is: gathering evidence.
- "Please pull all Active Directory logs from the last 11 months for me."
- "Has anyone updated the Excel spreadsheet with the firewall rules since April?"
- "We need to prove that employees who left in August were removed from all systems. Who has the tickets for that?"
This manual data search is extremely inefficient, extremely expensive, and above all: it leads to inconsistent data. Auditors are trained to find exactly these inconsistencies (e.g., when the number of servers in the cloud billing does not match the number in the submitted CMDB list).
What Does "Audit-Ready" Mean in 2026?
To escape this madness, your IT data must be "audit-ready." But what exactly does this term mean under the tightened conditions of NIS-2?
- Radical Completeness (No Exceptions): The auditor accepts no excuses for undocumented systems. Your data must traceably cover the entire infrastructure – from the central ERP system in the basement to AWS instances and the shadow IT of specialized departments. If your data collection process has gaps, the audit fails.
- Historical Continuity (The "Memory"): The most important criterion in 2026. As often emphasized, auditors today no longer check a snapshot. They check processes over time. Audit-ready data must have a tamper-proof history. You must be able to prove in Q4 what your IT landscape looked like in February. Those who only overwrite data states in their CMDB lose their evidentiary power.
- Connected Context: A simple list of 1,000 servers is worthless to an auditor. Audit-ready means you can point to a server and immediately prove: This server belongs to process X, is subject to protection requirement Y, and the responsible asset owner is employee Z. This context must be correct.
Use the Summer for Automation
If you realize now that your data does not meet these three criteria and you are heading toward the next Q4 war room, summer is your last chance for a course correction.
The solution lies in establishing an automated, API-driven "Single Source of Truth." If you implement an asset data platform like Qbilon now in July, the following happens:
- The system connects to your cloud providers, hypervisors, and security tools and creates a gapless, context-rich real-time inventory in just a few days.
- The decisive factor: From the day of implementation, the system begins to historicize every change (changes, new servers, deleted firewalls).
When the auditors arrive in November, you can look back on four months of a gapless, automated, and audit-proof data history. You don't have to lock experts in the war room. You open the dashboard, select the compliance policies required by the auditors (e.g., "All systems must be encrypted"), and export the evidence for the audit period at the touch of a button ("Push-Button Evidence").
Conclusion: Save Yourself the Stress
A year-end audit should be a professional discussion about risk management and not a hectic scavenger hunt for lost Excel files.
Use the third quarter strategically. Throw the manual lists overboard and invest in the automated foundation of your IT compliance. A data-driven, historicized CMDB completely takes the burden of evidence generation off your shoulders. Make the fourth quarter of 2026 the quarter in which you meet your auditors not with beads of sweat on your forehead, but with resilient data.