Detecting Shadow IT: How to Make the Invisible in Your Network Visible
The Democratization of IT
The democratization of IT is one of the greatest achievements of the last decade. To introduce new software or provide computing power, specialized departments today no longer have to go through a three-month approval process with IT procurement. An employee with a corporate credit card can sign up for a new SaaS (Software as a Service) subscription for the marketing team within five minutes; a developer can provision a new test environment in AWS with three lines of code.
This agility drives business forward – and at the same time drives the Chief Information Security Officer (CISO) to distraction. Because this democratization has created a huge, uncontrollable monster: Shadow IT.
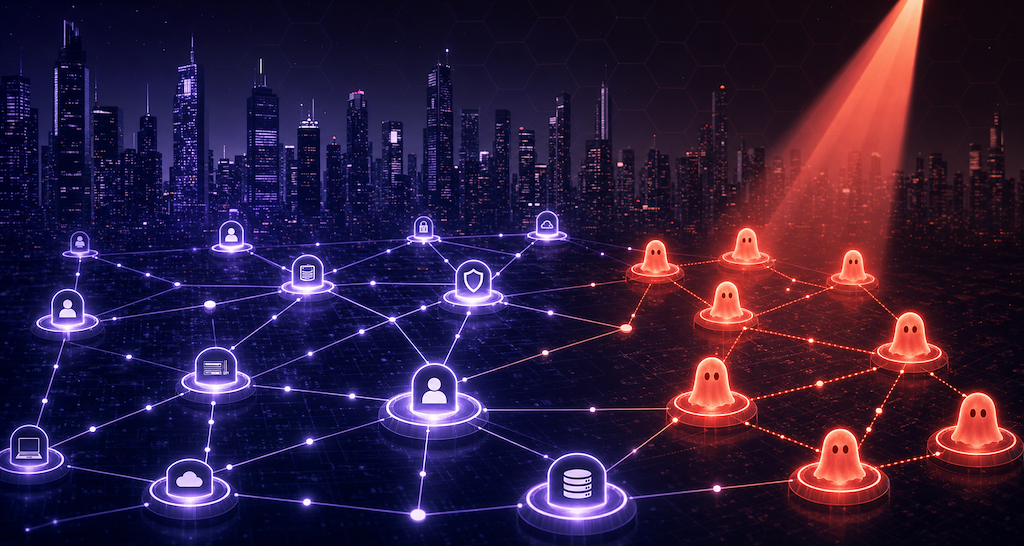
Shadow IT describes all hardware and software resources, cloud services, and networks used within a company without the central IT department knowing about them, approving them, or managing them. In this post, we reveal why shadow IT represents the single biggest risk to your compliance (NIS-2) and how you can finally make the invisible visible.
The Massive Dangers of the Unknown
Shadow IT is not a trivial offense. It systematically undermines all efforts regarding IT security, data protection, and cost control:
- The Blind Spot in Security Monitoring: If the Security Operations Center (SOC) doesn't know about the marketing department's new cloud server, that server will be neither captured by the vulnerability scanner nor protected by the central firewall. It is an open gateway for ransomware.
- Data Breach and GDPR: If employees upload sensitive customer data to an unapproved, cloud-based project management tool (like a private Trello or unsecured Dropbox board), the company loses all control over that data. A leak carries the threat of massive GDPR fines.
- Destroyed Audit Readiness (NIS-2): As we know, auditors under NIS-2 demand a complete asset inventory. If an auditor happens to stumble upon unauthorized systems during an audit (which almost always happens), the audit has basically already failed. The auditor must assume that the company's risk management is not functioning.
- Hidden Costs (FinOps): Shadow IT causes uncontrolled spending, as subscriptions often continue to run even if the tool hasn't been used for a long time.
Why Traditional Discovery Fails
The classic reaction of the IT department to the problem is: "We scan the network."
Typically, IP scanners (like Nmap) or agent-based discovery tools are used for this. This approach worked well in the past when the network still had clear boundaries (a perimeter). Today, in the cloud and SaaS era, it fails miserably.
Why?
- An IP scanner in the local corporate network will not find the SaaS application hosted on a third-party provider's servers.
- An agent-based security tool (which must be installed on every server) will not find the shadow server in the cloud – because where no agent is installed, no system can report back.
The traditional discovery paradigm – waiting for a device to "report in" to the network – is useless for shadow IT.
The API-Driven Solution: Correlation as the Key
To detect shadow IT, we need to act more intelligently. We must stop looking for the devices themselves and instead start analyzing the metadata and data traces these devices leave behind.
This is the core approach of a modern, automated asset platform like Qbilon. Instead of blindly searching the network, Qbilon integrates via APIs into the company's central nervous systems and compares this data (Data Correlation):
- Identity Correlation (Active Directory / Entra ID): Employees must log in to shadow SaaS services. Often, they use Single Sign-On (SSO) via their corporate account. Qbilon analyzes identity data: "Why are 15 employees from the HR department regularly logging into the application CloudServiceX when this application does not exist as an approved asset in our CMDB?" Shadow IT exposed.
- Cloud Billing Correlation: A developer has secretly opened an AWS account with his corporate credit card. Qbilon pulls central billing/invoicing data from ERP systems or the cloud master account and matches it with the CMDB inventory. "We are paying invoices for AWS Region Frankfurt, but according to the inventory, we have no authorized resources there." Shadow IT recognized.
- Network Traffic Correlation: By connecting to firewall logs or network traffic analysis (NetFlow), the platform detects when internal IPs send massive amounts of data to external, unclassified cloud storage services.
Conclusion: Regaining Control Without Destroying Agility
The goal of detecting shadow IT must not be to return the company to a bureaucratic prison where every software license has to wait three months for approval again. Business units need their agility.
The goal must be to create transparency. When departments use new services, central IT documentation must recognize this automatically and in real time. With platforms like Qbilon, you close the blind spot in your infrastructure. You bring the invisible to light, subject it to central security and compliance monitoring (NIS-2), and ensure that innovation and security finally go hand in hand.