When the Auditor Knocks: Evidence Generation at the Push of a Button
Imagine the following scenario: It's Tuesday morning, 9:00 AM. A calendar invitation pops up for the IT executives and the CISO. Subject: Kick-off meeting for the upcoming NIS-2 Compliance Audit. In most IT departments, this invitation triggers a collective sigh, followed by the mental preparation for four weeks of extreme stress. The so-called "Audit mode" is activated. The reason for this tension is rarely the concern that the company is insecurely positioned. The problem is not the actual security, but the burden of proof. In Audit terminology, this proof is called "evidence." And the manual generation of this evidence is one of the most expensive, frustrating, and error-prone processes in modern IT. In this post, we show you how to end this madness and make Audits a mere formality through automated "Push-Button Evidence."
The Anatomy of the Manual Search for Evidence
To understand the level of suffering, we must analyze how a typical evidence generation process works without an automated platform. The Auditor formulates a simple requirement, for example, according to BSI IT-Grundschutz or NIS-2: "Please prove that in the past six months, all Cloud instances that process customer data had active drive-level encryption (Encryption at Rest)."
The IT Team Begins the Data Hunt
- The Cloud team logs into AWS and Azure and exports page-long CSV files with all running instances and their storage configurations.
- The Security team must find out which of these thousands of IDs actually process "customer data." To do this, they interview application owners and dig through outdated CMDB entries.
- The Compliance team then tries to overlay these two worlds in a master Excel spreadsheet (VLOOKUP hell).
- The problem of history: The generated list only shows the status as of today. To prove the "past six months," administrators must manually parse and interpret backup logs or CloudTrail entries. This approach consumes vast amounts of full-time equivalents (FTEs). Highly qualified experts do the work of clerks. Furthermore, the result is prone to human error – and Auditors can smell inconsistent, manually "cobbled together" data from a mile away.
The Paradigm Shift: Push-Button Evidence
What does the alternative look like? The way out of Excel hell leads through the full automation of IT documentation in connection with historical data (Continuous Compliance). When a company uses a platform like Qbilon as its central IT hub, the evidence generation process changes radically:
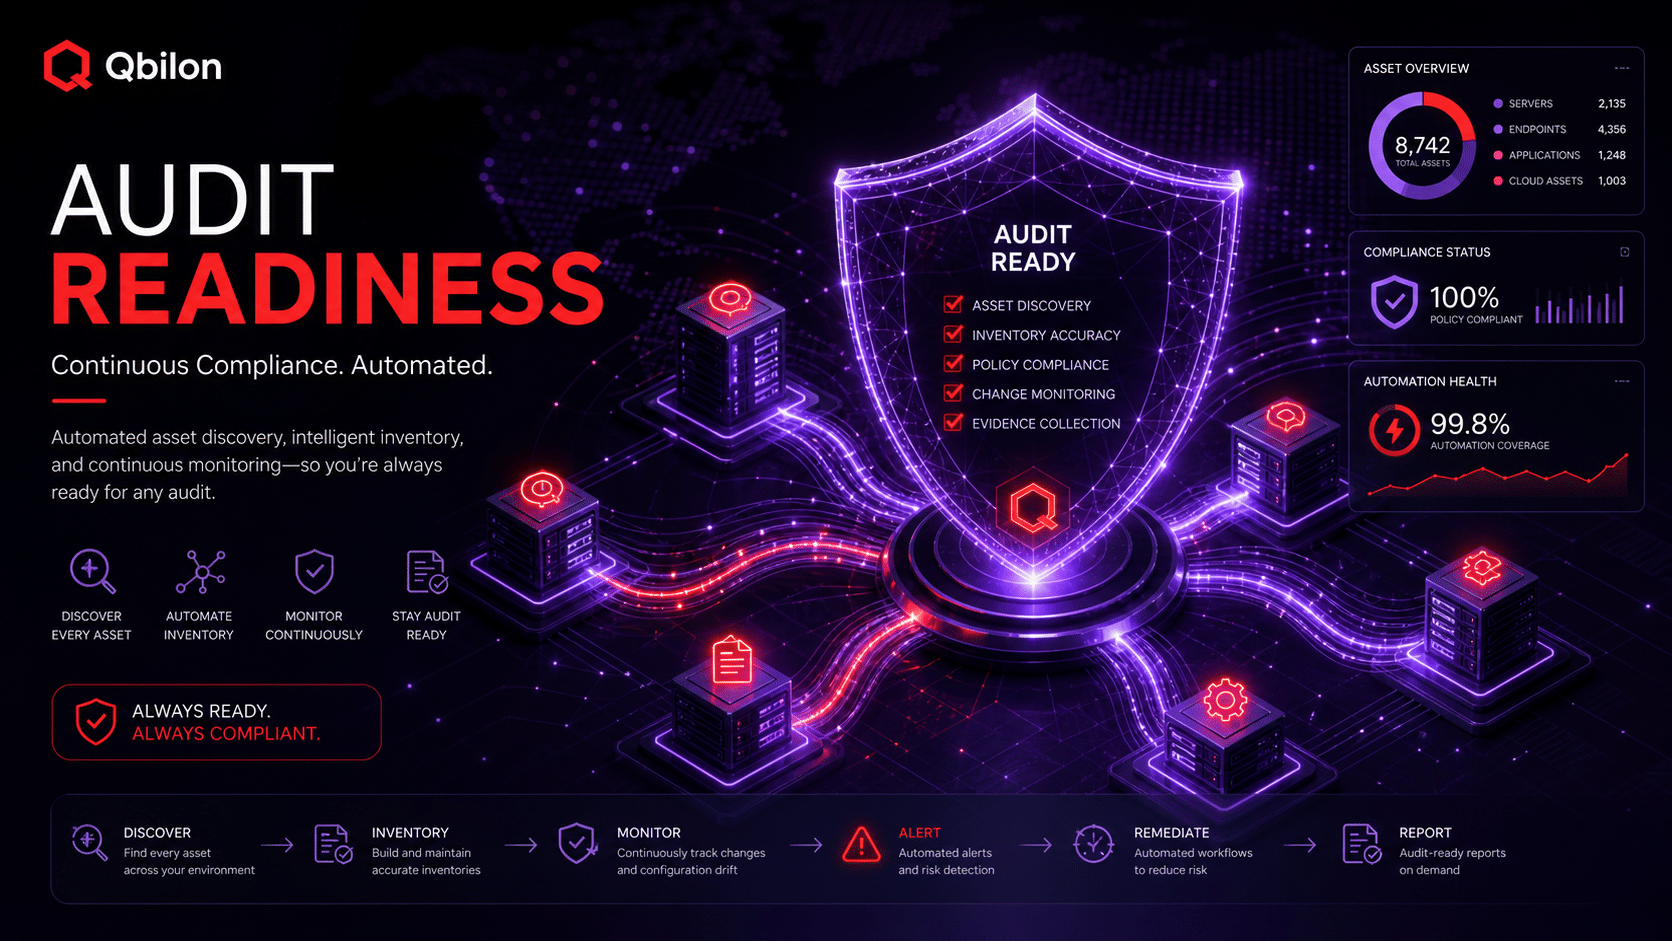
- The data is already there (and historized): The system does not have to be started only when the Auditor knocks. Through API integrations into the Cloud, the network, and security tools, Qbilon continuously monitors the infrastructure in the background. Every newly launched asset, every changed configuration (such as enabling or disabling disk encryption) is immediately recognized, timestamped, and stored in a tamper-proof time series.
- Automatic Mapping of Policies (Rules): In the platform, legal requirements are translated into technical rules (policies). The NIS-2 requirement becomes the rule: If Tag = 'CustomerData', then Property 'EncryptionAtRest' must = TRUE. The system checks this rule 24/7 fully automatically against the actual inventory.
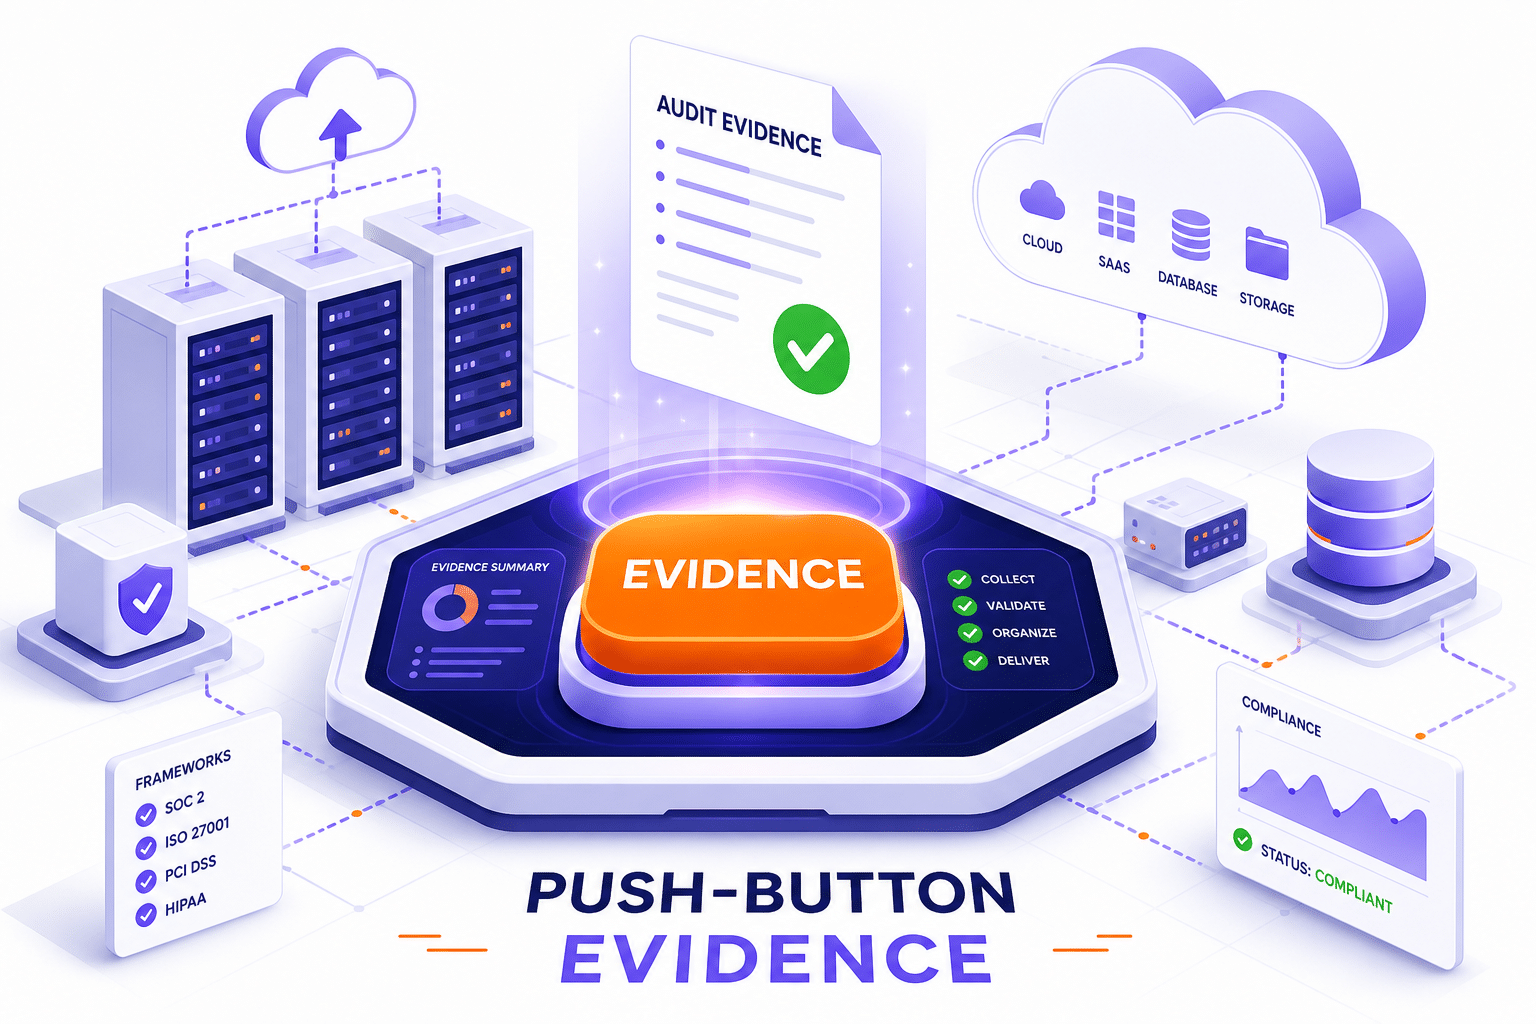
- The Push of a Button: If the Auditor now requests the said evidence for the last six months, the Compliance officer opens the dashboard. They select the "Drive Encryption Customer Data" policy, set the time filter to the last six months, and click "Export." Within fractions of a second, the platform generates a verified, graphically prepared, and historically flawless report. The report shows not only the perfect state of today but provides seamless proof that the policy was met every single day of the last 180 days. The Double ROI: Lower Costs, Increased Security Generating evidence at the push of a button brings companies a double return on investment (ROI): Massive Cost Savings: The time required for Audit preparation drops from several weeks to a few hours. IT specialists can return to their core tasks – improving architecture and defending against real cyberattacks instead of formatting spreadsheets. Psychological Relief: Audits lose their terror. Management and the CISO know at all times exactly where the company stands regarding Compliance (Audit-Readiness). Surprises during the auditor's closing presentation are a thing of the past.
Conclusion: Prove Your Excellence
Audits are important. They force organizations to critically question their security architectures and sharpen processes. But the presentation of proof must never paralyze the operational capacities of IT.
- The manual generation of evidence is a relic from a time when IT still consisted of a few dozen physical servers. In the era of Ephemeral IT, NIS-2, and the strictest KRITIS regulations, you need a system that collects the evidence for you fully automatically. With Push-Button Evidence, you don't just prove your Compliance – you prove operational excellence.