Breaking Down Data Silos – How to Unite Cloud, On-Premise, and OT in One View
If you ask CIOs or IT architects today to draw their infrastructure on a whiteboard, the result is rarely a simple, clear picture. The reality of modern enterprise IT resembles a complex spiderweb. There is the classic local data center (on-premise), there are public cloud environments with AWS and Microsoft Azure, hundreds of distributed SaaS applications, a fleet of employee laptops, and – especially in the manufacturing sector – a growing landscape of Operational Technology (OT), i.e., industrial control and production systems. This diversity (the best-of-breed approach) is intentional because it offers flexibility and drives innovation. However, it has a massive side effect: the creation of impenetrable data silos. Each of these environments comes with its own management and monitoring tool. This fragmentation destroys the holistic view of the company and becomes an insurmountable obstacle during security incidents, audits (NIS-2), and daily IT operations. In this post, we discuss why breaking down these silos is vital for survival and how to create a single “pane of glass” (a central view).
The Anatomy of the Silo Problem
How does this chaos arise? Quite naturally. The network team uses Cisco or Palo Alto dashboards to monitor traffic. The cloud team swears by the native AWS console and CloudWatch. The security team stares at the vulnerability scanner console or the EDR (Endpoint Detection and Response) system. And on the production floor, the plant operator maintains their own lists for the SCADA systems (OT).
- The problem: These tools do not talk to each other. A server named “instance i-12345” in AWS might only be listed as IP address “10.0.5.55” in the security scanner and billed as “Project-X-Webserver” in accounting. These isolated truths (multiple versions of the truth) lead to dangerous blind spots: Security Blind Flight: The security tool reports a critical vulnerability on an IP address. Without context from the cloud console and the CMDB, no one knows whether that IP hides an unimportant test server or the central interface to the production plant (OT). Prioritizing security gaps becomes a guessing game. Operational Inefficiency: During a network outage, experts from five teams sit together trying to compare screenshots from five different tools to find the cause. Troubleshooting is massively delayed. Impossible Compliance: As we know in the context of NIS-2, auditors demand seamless evidence for all assets. Manual consolidation of data from cloud, on-premise, and OT into an Excel spreadsheet is impossible due to the sheer volume and high rate of change. The Special Challenge: IT/OT Convergence
- The urgency of the silo problem is currently most evident at the interface between classic IT and Operational Technology (OT). Historically, computer networks in offices (IT) and machine control systems in the factory (OT) were strictly (often even physically) separated from each other (“air-gapped”). Today, these worlds are mergeing unstoppably in the course of Industry 4.0 and the Industrial Internet of Things (IIoT). Machines deliver real-time data to cloud servers, and production lines are maintained from home offices. This IT/OT convergence unlocks enormous efficiency potential but simultaneously opens up huge security gaps. Hackers today often no longer attack IT directly but use poorly protected, networked sensors or machines in OT to penetrate the corporate network. Asset management that is blind to the OT world is simply negligent in 2026. OT must urgently become part of the central IT documentation.
The Solution: An API-Driven Meta-Level
How do you solve the silo problem without taking away the specialized best-of-breed tools your teams are used to? The answer is not to introduce a gigantic new tool that is supposed to do everything (an approach that has often failed in the past due to enormous implementation costs).
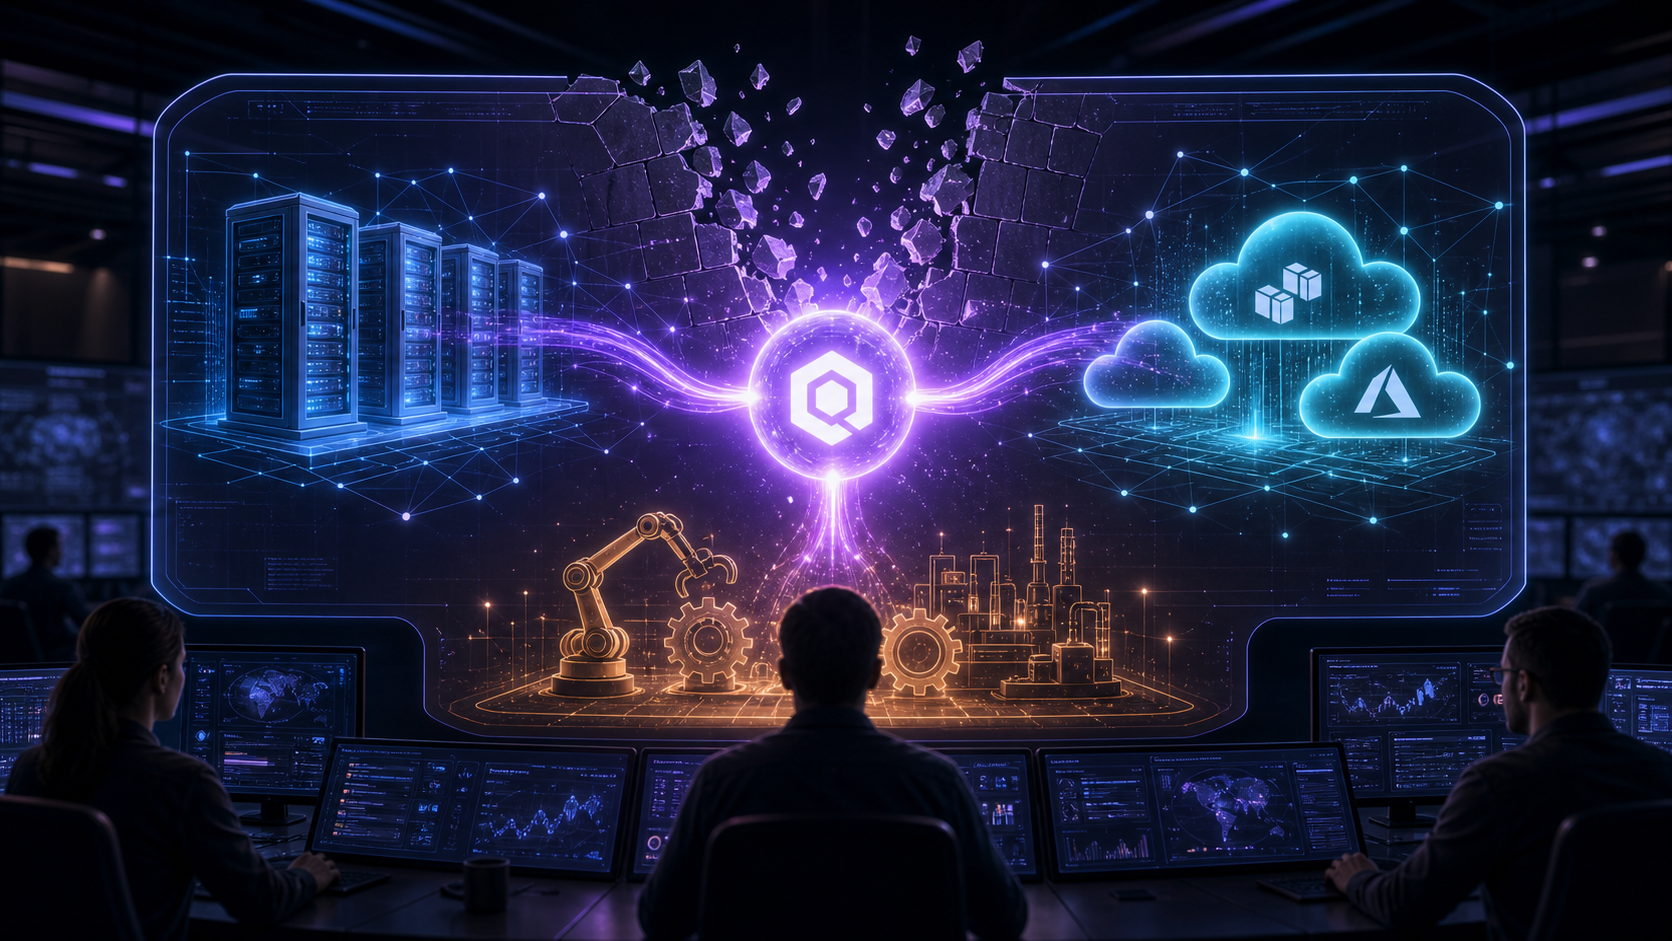
- The solution lies in establishing a meta-level that intelligently brings together data from all existing systems. This is exactly where the Qbilon platform positions itself as a central IT hub. Easy Integration (Connectors): Via standardized APIs and ready-made connectors, Qbilon plugs into vCenter, AWS/Azure, network scanners, security tools, and OT monitoring systems. Normalization: The system recognizes that “instance i-12345” from AWS and “IP 10.0.5.55” from the security scanner are one and the same physical asset and merges this data into a consolidated, “golden” data record. Uncovering Relationships: Suddenly, it becomes visible how the cloud application communicates with the local database server and which industrial robot (OT) is controlled by that database server.
Conclusion: He Who Sees the Whole Is in Control
Data silos are the natural enemy of security, efficiency, and compliance. As long as your administrators and security experts are forced to jump back and forth between a dozen different dashboards, you will always be chasing the complexity of your infrastructure. With an automated asset data platform, you break down these silos. You create a single, high-resolution “single source of truth” that unites cloud, on-premise, and OT in a clear, historized view. Only when you can see the entire playing field can you fix errors quickly, pass audits confidently, and proactively defend your network.