The Concept of the "Single Source of Truth" in Enterprise Architecture Management (EAM)
Enterprise Architecture Management (EAM) is considered the supreme discipline of IT in many companies. Enterprise architects are the urban planners of the organization: they design the IT development plans of the future, plan complex Cloud migrations, harmonize the application landscape after corporate mergers (M&A), and align IT strategically with the company's goals. Yet as high-flown as this task sounds, the daily life of an enterprise architect is often frustrating in practice. The reason for this is a fundamental lack of data. Many EAM initiatives do not fail due to a lack of strategic vision, but because of a trivial question: "What does our IT landscape actually look like today, at this exact moment?" In this post, we shed light on why classic EAM, which relies on manual Visio drawings and manually maintained CMDBs without real-time updates, is at a dead end. We demonstrate how the concept of the "Single Source of Truth" releases Enterprise Architecture Management from its ivory tower and turns it into a measurable, data-driven driver of value creation.
The "Garbage In, Garbage Out" Problem in EAM
To plan a digital transformation (target state), you absolutely must know where you are starting (current state). This is exactly where the problem lies. In traditional EAM setups, architects spend an absurd amount of their working time requesting data from department heads, consolidating Excel lists, and typing application portfolios into tools.
- The result of this months-long process is architecture documentation that is already hopelessly outdated the day it is completed. In the meantime, the Cloud department has rolled out three new microservices, and the security team has taken outdated Servers offline.
- If the enterprise architect now plans a migration based on this outdated data, collisions are inevitable. If the data base is garbage, the strategic planning is also garbage ("Garbage In, Garbage Out").
What is a "Single Source of Truth" (SSoT) Really?
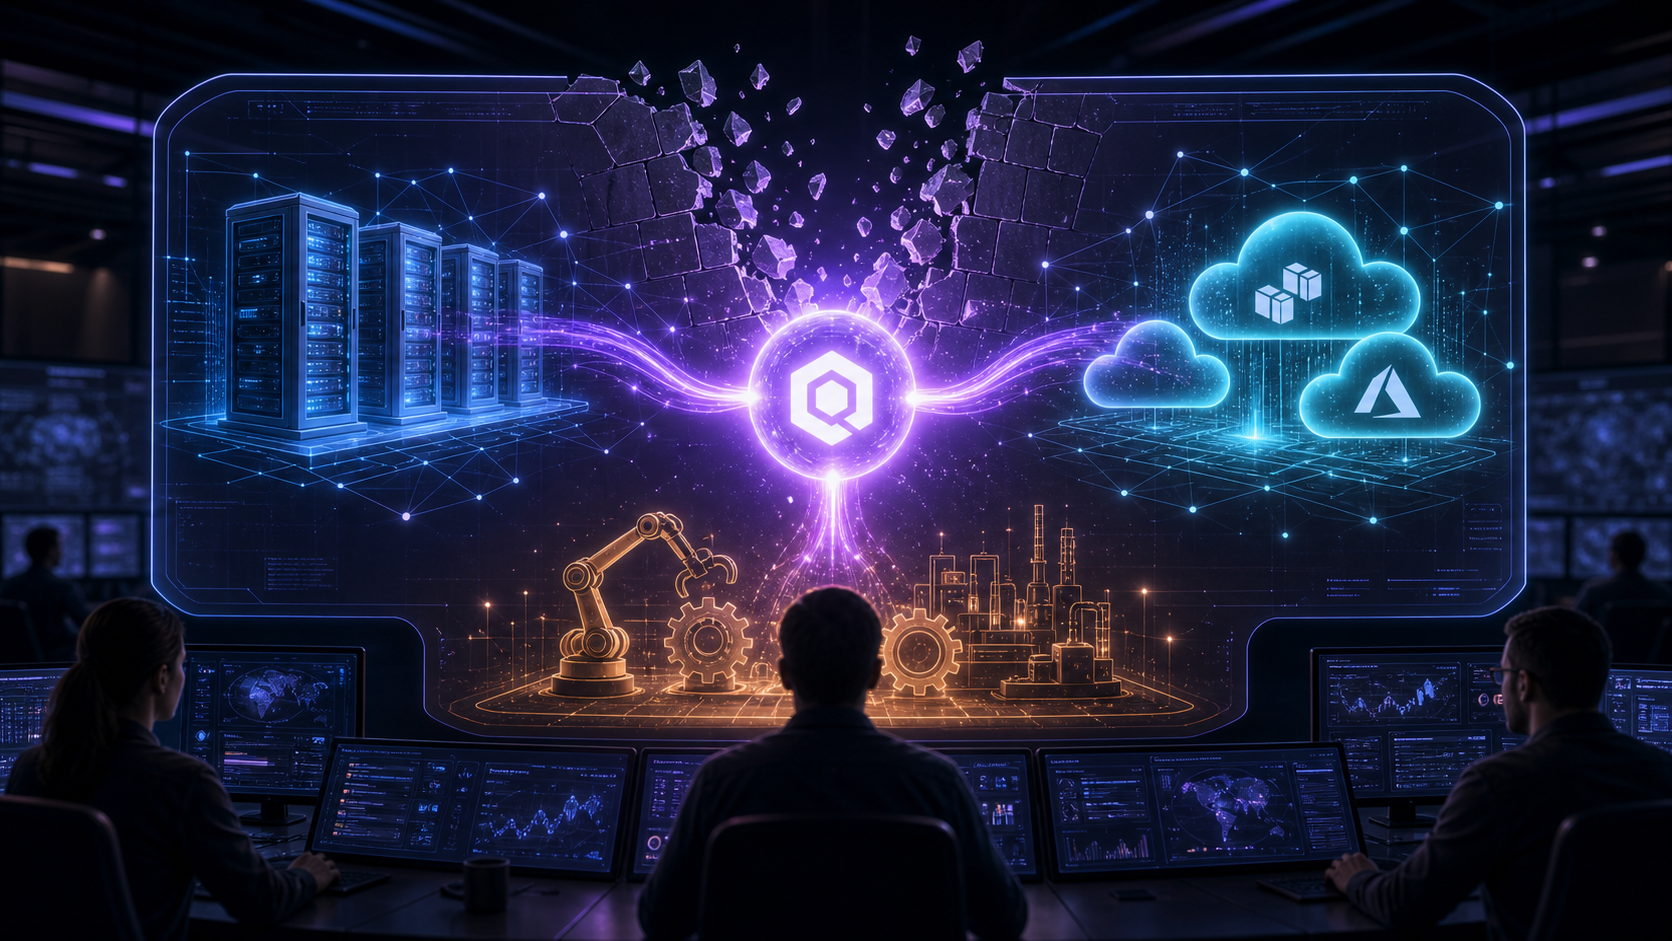
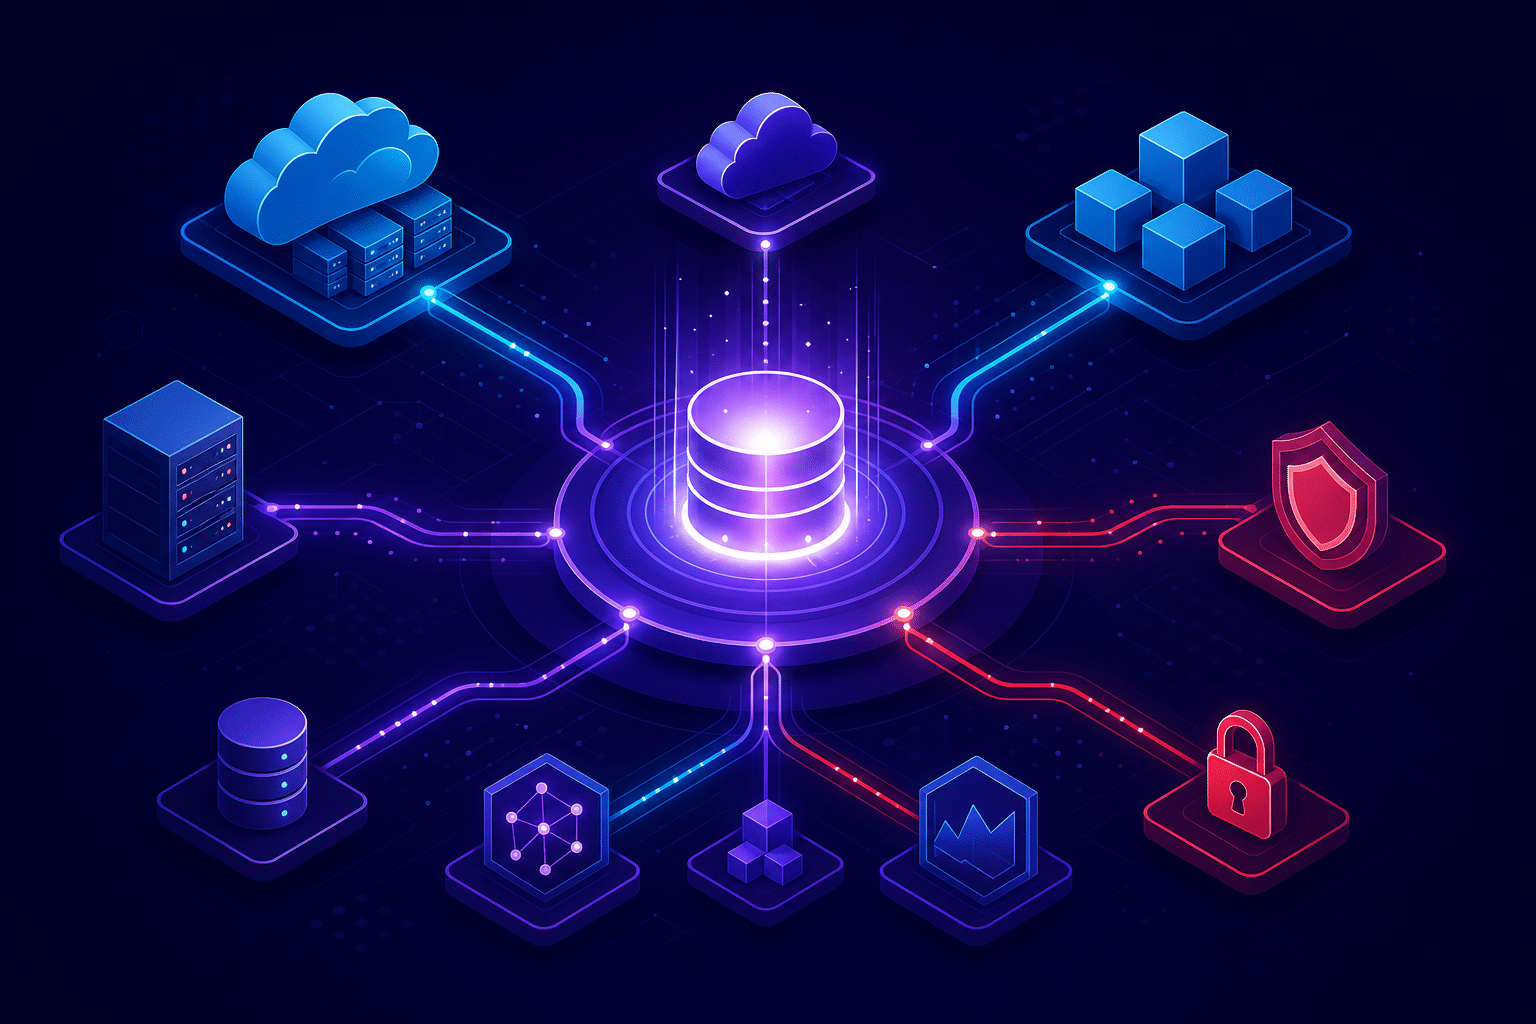
The term "Single Source of Truth" is often misunderstood. It does not mean that a company is suddenly only allowed to use a single, giant piece of software in which network admins, security analysts, and architects must all work equally. That would be utopian. Experts should continue to use their highly specialized best-of-breed tools (AWS console, Cisco dashboards, vulnerability scanners). A true SSoT is rather an intelligent meta-data layer. A platform like Qbilon acts as precisely this layer. It continuously and automatically extracts raw operational data from various IT silos via interfaces (APIs), normalizes it, cleans up duplicates, and links it together. In this way, operational reality (ITOM), Sicherheit (Security) status, and the strategic portfolio view (EAM) merge into a single, consistent, and historized model.
The Advantages for the Enterprise Architect
When EAM is based on an automated "Single Source of Truth," the way architects work and their impact change dramatically: Data-Driven Impact Analysis (Dependency Analysis): If an outdated core application is to be replaced by a SaaS solution, the architect needs to know which systems, databases, and business processes (Business Capabilities) are attached to the old application. With an SSoT, months of guesswork are eliminated. The system provides architecture dependencies in real time based on actual network communication. The risks of migration become immediately measurable. Application Portfolio Management (APM) in Real Time: Spotting redundancies is a core task of EAM. Why are we running three different CRM systems in the company? An automated inventory (including shadow IT) uncovers these duplicate structures. The architect can demonstrate cost reduction potential (Application Rationalization) supported by data and present a clear business case to management. Integration of Security (Security by Design): Traditionally, security in EAM is often only considered at the end of a project. With an SSoT, the architect can see during the inventory which legacy systems are chronically affected by vulnerabilities (vulnerability data directly in the EAM dashboard). This enables a consistent transformation towards a "Secure by Design" architecture and massively assists in complying with the requirements of the Cyber Resilience Act (CRA), which has already entered into force and whose full requirements will become binding from December 2027.
Conclusion: Out of the Ivory Tower
Enterprise Architecture Management is not an end in itself and must not be an academic exercise in abstract modeling tools. It must solve real problems. However, this only succeeds if the architecture models are not based on estimates, outdated tables, or isolated CMDBs, but on the unvarnished technical reality. By establishing an automated Asset data platform like Qbilon as a "Single Source of Truth," companies finally give their architects the tool they need. Data-driven EAM closes the gap between IT operations, cyber security, and management strategy – and thus becomes a reliable navigator for every digital transformation.