CRA and Patch Management: Why Missing Asset Knowledge Leads to Liability Risks
Cyber Resilience Act: Why Patch Availability Becomes a Liability Trap Without Asset Knowledge
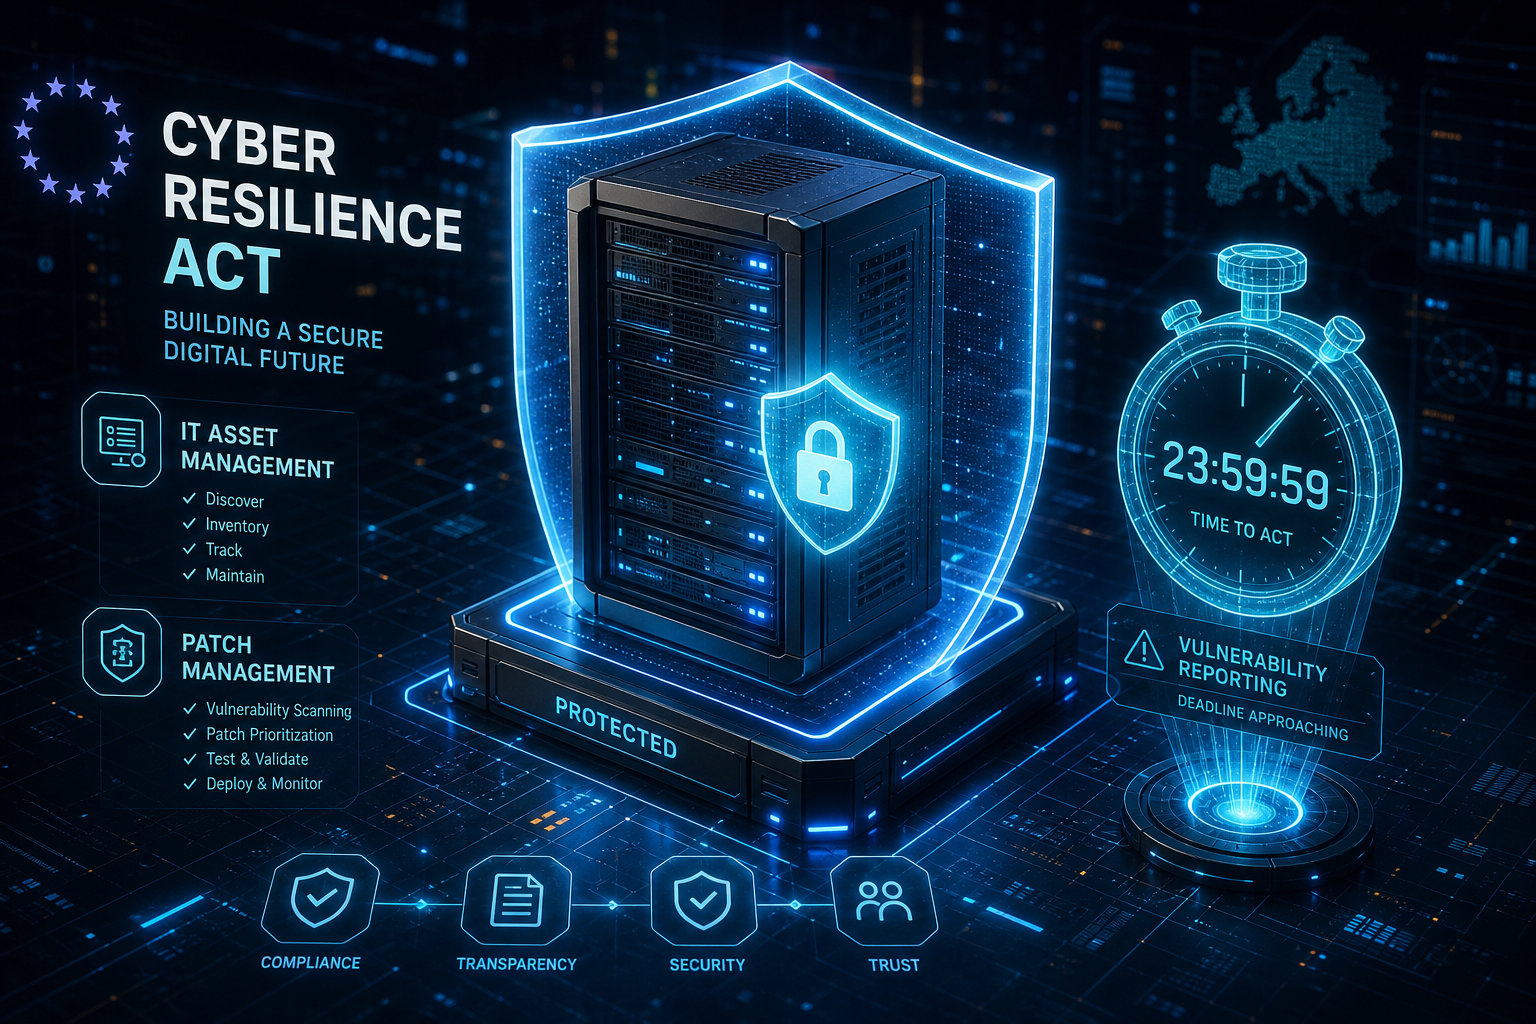
The upcoming European Union Cyber Resilience Act (CRA) will radically transform the IT market. From a cybersecurity perspective, the fundamental idea of the law is a blessing: manufacturers of hardware and software with digital elements will be forced in the future to develop their products securely from the ground up (Security by Design) and, even more importantly, to actively close security vulnerabilities free of charge via updates (patches) over a defined period of at least five years.
Many IT managers on the operator side (i.e., the software users) are looking forward to this new era. The expectation: finally, manufacturers must ensure secure software, and our networks will automatically become more secure!
This assumption is a dangerous fallacy. The CRA solves the problem of vulnerable software, but at the same time, it creates a massive new liability trap for the operator's IT management. In this post, we explain why the availability of patches is completely useless if you do not know your own infrastructure, and how missing asset knowledge will lead to direct legal consequences in 2026.
The Shift in the Liability Chain
To understand the new risk, we must look at how security incidents have often been handled until now. If hackers used a previously unknown vulnerability (zero-day exploit) in a software to penetrate a company, the culprit was quickly found by the IT department (and often by management): the software manufacturer. "We couldn't protect ourselves; there wasn't a patch yet!" was the classic, often legally tenable line of defense.
With the entry into force of the CRA, this narrative changes drastically. The law forces manufacturers to proactively search for vulnerabilities, report them to the European Union Agency for Cybersecurity (ENISA), and provide updates within the shortest possible time. At the same time, the transparency obligations of the CRA (keyword: SBOMs, Software Bill of Materials) generate a flood of publicly known and cataloged vulnerabilities (CVEs).
The new scenario looks like this: The manufacturer identifies a vulnerability, releases the patch, and publishes the risk. At exactly this moment, an invisible stopwatch starts ticking. Cybercriminals now also know about the gap and immediately begin (often within 24 hours) scanning the internet automatically for unpatched servers.
The manufacturer has fulfilled its legal duty (CRA). Liability (and risk) transfers entirely to you, the operator, at this moment.
The Patch Management Nightmare Without CMDB
If you are now hacked through this known, patchable vulnerability and have to account for it to the board, your customers, or the data protection authority (within the framework of NIS-2 or GDPR), you can no longer rely on the manufacturer. The piercing question will then be: "The patch has been available for four weeks. Why didn't you install it?"
In companies without automated, historized asset management, the bitter but honest answer is usually: "We didn't know which of our 1,200 servers this affected software was installed on."
This lack of visibility is no longer a valid legal defense – it is evidence of gross negligence. If you want to roll out updates (patches) today, you will encounter insurmountable hurdles without a reliable data basis (CMDB):
- The Blind Spot: You patch the 90 servers listed in your manual Excel list. You forget the 10 shadow IT servers running in AWS. The hacker finds exactly these 10 servers.
- Fear of Downtime: You may know that the vulnerable software is running on Server 04, but you don't know which business processes depend on it. For fear of paralyzing production by restarting the server, you postpone the patch window by three weeks. In week two, the hacker strikes.
Automation as a Legal and Operational Shield
To make patch management manageable (and legally secure) in the era of CRA and NIS-2, you must close the gap between the existence of a patch and its installation. The key to this is context, delivered by an automated asset management platform.
With systems like Qbilon, patch management turns from a blind search mission into a precise, surgical measure:
- Real-time Correlation: As soon as the manufacturer (or the NVD database) reports a vulnerability, Qbilon matches this information with your always up-to-date asset inventory. You immediately see on the dashboard: "The vulnerable library is running exactly on instances AWS-WEB-01 to AWS-WEB-15."
- Risk Prioritization Through Dependencies: The platform shows you that AWS-WEB-01 to 05 are connected to business-critical, externally accessible customer portals. These must be patched immediately (within hours). AWS-WEB-15 is an internal test server without internet access; the regular maintenance window on the weekend is sufficient here.
- Historical Evidence: After patching, the historization function (Time Machine) records that the update was successfully installed on all 15 systems on August 14th at 11:30 AM. Watertight proof for any audit.
Conclusion: Accept the Responsibility
The Cyber Resilience Act holds manufacturers accountable but does not automatically provide you with a secure network. It merely provides you with the urgently needed building blocks (patches and SBOMs).
It is up to you to fit these building blocks quickly and accurately into your infrastructure. Anyone still trying to operate patch management in 2026 based on word-of-mouth, manual Excel lists, and a lack of architectural knowledge is playing Russian roulette with the company's liability. Automated, context-rich asset management is the only way to keep up with the pace of cybercriminals and protect your company from harm – both operationally and legally.