
From IT Chaos to Control: A Success Story
From IT Chaos to Control: A Success Story
It is Tuesday, October 14, 8:30 AM. A heavy silence fills the conference room on the 4th floor of a medium-sized engineering company. At the head of the table sits the external auditor for the upcoming NIS-2 pre-audit. He looks up from his laptop and asks the IT manager a seemingly simple question: "Can you please provide me with a complete list of all cloud instances that have access to your production data and prove that they have been patched without gaps over the last six months?"
The IT manager looks to his cloud architect. The architect looks to the security analyst. A nervous clearing of throats follows. The honest answer is: We don't know.
This scene, or very similar variations of it, has played out in countless companies in 2026. It often marks the absolute low point in IT management – but fortunately, it also marks the turning point. In this post, we tell the typical success story of a transformation. It is the journey from "best-effort chaos" to absolute, data-driven control through a Unified Asset Data Platform.
The Diagnosis: Silo Syndrome
After the failed pre-audit, the company began researching the root causes. Why didn't they know the answer? The IT department wasn't lazy or incompetent. Administrators were working 50 hours a week, and the budget for firewalls and security tools (EDR) was high.
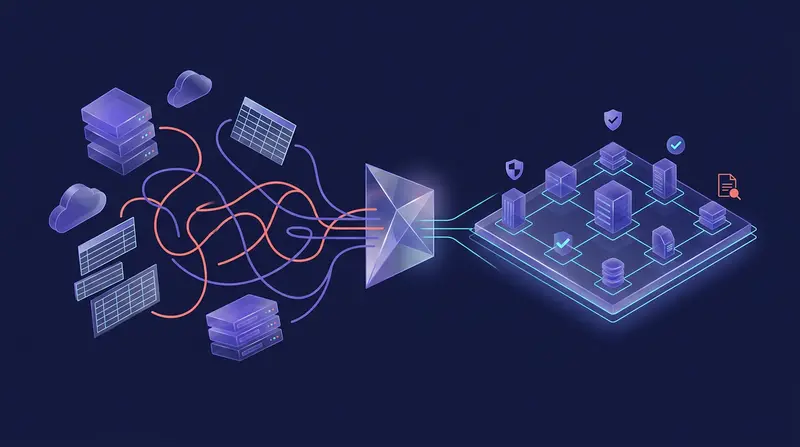
The diagnosis was Silo Syndrome. The IT operations team maintained the asset inventory manually in massive Excel spreadsheets and an outdated ITSM tool. Developers were rapidly provisioning new environments in AWS (Infrastructure as Code) – and only reporting this to IT sporadically. The security team, in turn, saw thousands of red alerts in their vulnerability scanner but couldn't map these IPs to any business process.
There was no "Single Source of Truth." Every department had its own incomplete reality. The result was a massive attack surface (shadow IT, orphaned assets) and an absolute inability to pass an audit.
The Turning Point: Automation instead of Excel
It became clear to the IT manager: if he ordered the Excel lists to be maintained even more accurately now, the problem would be back in three months. The process itself was broken. The decision was made for a radical technological cut: the introduction of an automated asset management platform (like Qbilon).
Step 1: API Discovery (Shedding Light on the Dark)
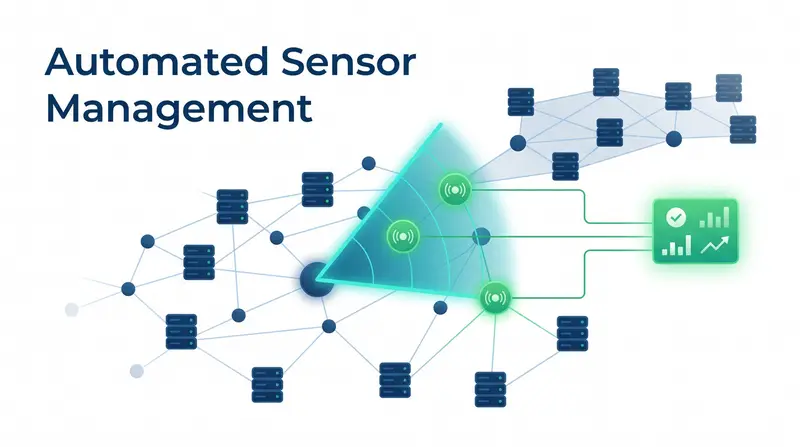
Instead of deploying new software agents to servers (agent bloat), the team integrated the new platform via APIs. Within a few days, VMware vCenter, the AWS dashboard, Active Directory, and the Tenable vulnerability scanner were connected. The "Aha!" moment was shocking and liberating at the same time: the platform revealed that the company was not operating 800 servers – as noted in Excel – but 1,150. The 350 unknown systems were forgotten test environments, unauthorized shadow IT, and orphaned cloud resources (orphaned assets) that not only caused enormous costs but were also wide open to attack.
Step 2: CAASM in Action (Closing the Gaps)
With new, 100% knowledge of the infrastructure, the security team launched its Cyber Asset Attack Surface Management (CAASM) strategy. The platform immediately displayed "coverage gaps": 120 servers in the cloud were missing the mandatory antivirus agent (EDR). These blind spots were closed within a week. At the same time, the platform reduced alert fatigue. Instead of working through 10,000 vulnerabilities, the team used dependency mapping (the dependency analysis of the CMDB) to identify the 20 vulnerabilities that were truly business-critical and reachable from the internet. Risk mitigation increased drastically, and stress within the team decreased.
Step 3: Continuous Compliance (The Auditor Returns)
The most important shift, however, happened in the background. From the day of implementation, the platform began to timestamp every single change in the network (new servers, changed firewalls, patches) (historization / time machine).
The Happy Ending: Evidence at the Touch of a Button
Six months later. It is April 2027. The same auditor sits in the same conference room for the final NIS-2 audit. He asks the same question about the patch history of the cloud instances.
This time, there is no nervous throat clearing. The IT manager opens his Qbilon dashboard, clicks on the stored compliance policy ("Patching Critical Infrastructure"), selects the period of the last six months, and exports a PDF. He hands the auditor the historically complete, machine-verified proof.
The auditor is satisfied. The certificate is granted. The audit, which used to mean four weeks of war-room meetings and panic, is completed in a few hours.
Conclusion: Become the Hero of Your Own Story
This transformation is not fiction. It is the exact process that companies are currently undergoing when they dare to make the leap from manual administration to data-driven IT governance.
The path from IT chaos to control begins with a simple decision: stop wasting your time managing spreadsheets. Invest in API-driven automation, connect your silos into a CAASM-capable "Single Source of Truth," and take back control of your hybrid IT landscape.